GDPR compliance means meeting the requirements of the EU's General Data Protection Regulation whenever you collect or use personal data about people in the EU. In practice, that means having a lawful basis for every use of personal data, being transparent about it, honoring people's rights, keeping data secure, reporting breaches, and being able to prove all of it.
What Is the EU General Data Protection Regulation (GDPR)?
By now, you've likely heard of the European data protection regulation, but may not fully understand the general requirements of GDPR — especially if your company operates outside of the EU.
Considered the most significant privacy regulation in 20 years, this set of regulations — in effect since May 2018 — is a substantial step up from the EU's previous data protection directive.
The new initiative transforms how organizations in every sector handle personal data and, for the first time, gives people a say over who collects their data, when it's collected, and how it's used.
With this regulation, companies can't just clean up the mess and say "sorry" after a personal data breach that affects sensitive data. They also can't collect and use consumer data without oversight or plainly worded disclosures. Stiff GDPR fines and penalties now exist for data breaches and data privacy violations.
To prove your organization's compliance with the GDPR, you must take steps to protect a data subject’s privacy from the get-go. Transparency is the name of the game — a new notion to many organizations that have traditionally put data privacy on the back burner.
GDPR compliance can seem overwhelming, but in the long-term, we expect to see better user/customer experiences, fewer data breaches, and greater trust between consumers and organizations regarding personal data.
Who Has to Comply With the GDPR?
The GDPR applies to any organization established in the EU that processes personal data. It also applies to organizations outside the EU, including U.S. companies, when they offer goods or services to people in the EU or monitor their behavior, such as tracking how EU visitors use a website (Article 3).
Company size doesn't change whether the GDPR applies. A few obligations, like keeping records of processing, have narrow exceptions for organizations with fewer than 250 employees, but the core rules apply to everyone in scope. If you're a U.S. business weighing whether this applies to you, our guide to GDPR compliance in the U.S. walks through the scenarios.
The 7 Principles of GDPR
Article 5 of the GDPR sets out seven principles. Every other requirement in the regulation traces back to one of them.
- Lawfulness, fairness, and transparency: Have a legal basis for processing, don't use data in ways people wouldn't reasonably expect, and tell them clearly what you're doing.
- Purpose limitation: Collect data for specific, stated purposes and don't reuse it for incompatible ones.
- Data minimization: Collect only what you need for those purposes.
- Accuracy: Keep personal data accurate and up to date, and fix or delete what's wrong.
- Storage limitation: Keep data in identifiable form only as long as you need it.
- Integrity and confidentiality: Protect data with appropriate security against unauthorized access, loss, or damage.
- Accountability: Be able to demonstrate that you comply with all of the above.
Accountability is the principle teams tend to underestimate. Regulators expect documentation: records of processing, policies, assessments, and the reasoning behind your decisions.
How to Get GDPR Compliant: 10 Steps
There's no single certificate that makes an organization "GDPR compliant." Compliance is an ongoing program, and most organizations build it in roughly this order.
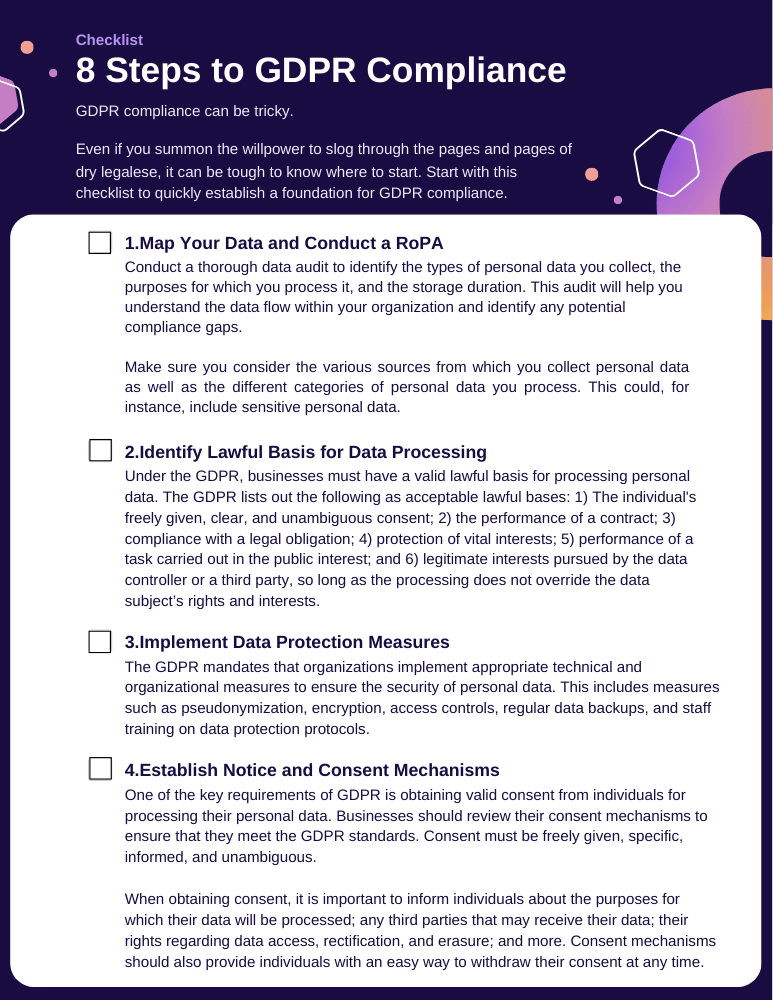
- Map your personal data. Find out what personal data you hold, where it lives, where it comes from, and who you share it with. This becomes the backbone of your record of processing activities (RoPA).
- Pick a lawful basis for each purpose. The GDPR gives six: consent, contract, legal obligation, vital interests, public task, and legitimate interests. Consent is only one of them, and it isn't always the right one.
- Update your privacy notice. Explain in plain language what you collect, why, your lawful basis, how long you keep it, who receives it, and how people can exercise their rights.
- Get valid consent where you rely on it. Consent has to be freely given, specific, informed, and unambiguous, and it has to be as easy to withdraw as it was to give. For website cookies and trackers, the EU's ePrivacy rules generally require consent before non-essential cookies are set. Not sure what your banner does today? A free Compliance Check scan flags dark patterns that can invalidate consent.
- Set up a process for data subject requests. You generally have one month to respond to requests to access, delete, or correct personal data. Our guide to DSARs covers the details.
- Manage your vendors and data transfers. Sign data processing agreements with your processors (Article 28), and use a valid transfer mechanism, such as Standard Contractual Clauses, when personal data leaves the EU.
- Secure the data and plan for breaches. Put appropriate technical and organizational security measures in place, and have a response plan that can meet the 72-hour notification deadline.
- Assess high-risk processing. Run a data protection impact assessment (DPIA) before you start processing that's likely to pose a high risk to people.
- Decide whether you need a DPO or an EU representative. Each is required only in certain situations, covered in need-to-knows #4 and #10 below.
- Document and review. Keep records that show how you comply, train your staff, and revisit the program as your use of data changes.
Want a version you can work through with your team? Grab our GDPR compliance checklist.
The 12 Need-to-Knows When It Comes to GDPR Compliance
Since its advent in 2018, many have celebrated the General Data Protection Regulation: In terms of protecting people’s privacy, it’s a game-changer (and a big one) that defines how to process data. But for the countless companies attempting to navigate all of its nuances and layers, the GDPR can cause confusion and, for many, frustration.
To help you understand it better, we’ve compiled a list of essential facts about GDPR rules and regulations. Use these as your guide to improving your organization's data security, protecting your data subjects' personal information, and avoiding non-compliance issues. We recommend reviewing the need-to-knows below but have also condensed these steps into a helpful GDPR compliance checklist you can access.
1. While the GDPR is mandated by the EU, it affects every country.
The European Parliament approved the General Data Protection Regulation in 2016 to replace a data protection initiative from 1995, but changes weren't enforced until 2018. For U.S. companies that believe they’re exempt from GDPR because they don’t do business with folks across the pond, think again.
The GDPR changes apply as much to countries outside the EU as they do to EU member states. If any organization, EU or otherwise, offers goods or services to EU data subjects or monitors their behavior, they're on the hook. This helpful checklist from GDPR.eu prepares U.S. companies for the associated regulations and requirements.
2. The GDPR applies to most kinds of personal data.
GDPR requirements govern almost every data point an organization collects, across every conceivable online platform, especially if it's used to uniquely identify a person. The GDPR also includes data routinely requested by websites, like IP addresses, email addresses, and physical device information. Types of personal data protected under GDPR include:
- Basic identity information
- Web data (like location, IP address, cookie data, and RFID tags)
- Health and genetic data
- Biometric data
- Racial or ethnic data
- Political opinions
- Sexual orientation
- Any information that relates to an identified or identifiable living individual
As you can imagine, "basic identity information" is a broad category. It includes user-generated data, like social media posts, personal images uploaded to websites, medical records, and other uniquely personal information commonly transmitted online. Yes, that means organizations must protect your tweets and Facebook statuses.

3. GDPR posits that users have 8 basic rights regarding personal data and data privacy.
The GDPR establishes eight rights that apply to all users. To achieve compliance, your organization must respect the following rights or face severe penalties:
The right to access: Individuals may request access to their personal data. They may also ask about how their data is used, processed, stored, or transferred to other organizations. You must provide an electronic copy of the personal data, free of charge, upon request.
The right to be informed: Individuals have the right to know what personal data you collect, why you collect it, how long you keep it, and who you share it with, usually through a clear privacy notice.
The right to data portability: Individuals can get the data they provided to you in a commonly used, machine-readable format and have it transferred to another provider. This applies when you process that data by automated means based on their consent or a contract.
The right to be forgotten: In certain circumstances, such as when the data is no longer needed or they withdraw their consent, individuals are entitled to erasure of their personal data.
The right to object: Individuals can object to processing based on your legitimate interests or a public task, and you must stop unless you can show compelling legitimate grounds that override their interests. Objections to direct marketing have no exceptions: processing for that purpose must stop.
The right to restrict processing of personal data: Individuals can ask you to stop processing their data or stop a certain kind of processing. Their data can remain in place if they choose.
Rights related to automated decision-making: Individuals have the right not to be subject to decisions based solely on automated processing, including profiling, that have legal or similarly significant effects on them, with limited exceptions.
The right to rectification: Users can request that you update, complete, or correct their personal data.
These rights give individuals considerable power over their data. They now have myriad tools to limit and prohibit organizations from using their personal information.

4. If you have no EU presence, you may need to designate a representative in the European Union.
If your U.S. company falls under the GDPR because it sells to people in the EU or monitors their behavior online, and it doesn't have an establishment in the EU, Article 27 generally requires you to designate a representative there. There's a narrow exception for occasional processing that's unlikely to put people at risk and doesn't involve sensitive data at large scale. A representative in the European Union exists to contact EU supervisory authorities and data subjects, plus maintain processing records.
If you don't already have a subsidiary, corporate affiliate, or external data protection officer in EU territory, you can name an unaffiliated person or entity. Consider a "GDPR Representative as a Service," where you pay a U.S. company a flat fee to name one of their EU representatives to act as yours. Then, you list them as your EU contact to satisfy the GDPR. It's a fast way to meet the Article 27 requirement, and it's a service Osano offers.
5. Ignoring or evading GDPR compliance can cause hefty penalties.
The GDPR is a complete shift in thinking, and it's safe to say many U.S.-based organizations are still scratching their heads. Organizations had a two-year runway between the regulation's adoption in 2016 and enforcement in May 2018, but that runway is long gone.
These days, companies must at least prove to officials that they’re actively working toward accountability and compliance. GDPR fines are tiered: up to €10 million or 2% of worldwide annual turnover for violations like security or record-keeping failures, and up to €20 million or 4% for violations of the core principles, lawful basis, consent conditions, or individuals' rights. In each tier, the higher of the two amounts applies.
6. When you rely on consent, it has to be opt-in.
When consent is your lawful basis for processing, the GDPR requires affirmative, “opt in” consent. Pre-checked boxes, silence, and inactivity don't count.
Instead of assuming user consent (by opting them in automatically and providing an opt-out method), you must get a clear yes before you collect, store, and process their personal data for that purpose. Email marketing has its own wrinkle: the EU's ePrivacy rules generally require opt-in consent for marketing emails, with a limited exception in many countries for existing customers who bought similar products.
Additionally, users don't just have the right to decide whether you collect and use their data; they can also determine how you use it. They have the legal right to question and appeal on how their personal information is presented to themselves and others.
For instance, a user might object to Google's use of their data to refine their algorithm and show content to other users. Or a user might choose to opt out entirely at any point due to their right to be forgotten — in which case, it's your responsibility to scrub their data from your systems.
Is your consent banner doing what you think it is? Osano's free Compliance Check scans your website for dark patterns that can invalidate consent, checks how your site handles signals like Google Consent Mode and Global Privacy Control, and looks for an up-to-date privacy policy and a way for people to submit rights requests. Request a free scan.
7. You can’t dodge GDPR obligations by hiding behind legalese.
Does anyone read a data privacy policy, let alone its fine print? Not often.
It’s possible people aren’t reading privacy policies because, too often, they can be tangled webs of legal jargon. For that reason, the GDPR prohibits organizations from hiding behind illegible terms and conditions that are difficult to understand.
Instead, the GDPR requires organizations to clearly define their data privacy policies and make them easily accessible. They must explain how they engage in personal data processing and what they do with it. Further, they can't write privacy policies that absolve them from responding to a data breach.
There's another caveat: Your organization must also know and monitor your vendors (and their privacy policies) to confirm they handle your EU subject data properly. Under the GDPR, you could be held accountable for their compliance (or lack thereof).
8. Under GDPR, time limits are set for breach notifications.
When a personal data breach occurs, the controller must report it to the relevant supervisory authority within 72 hours of becoming aware of it, unless the breach is unlikely to put people's rights at risk. Processors must notify the controller without undue delay. If the breach is likely to pose a high risk to individuals, the controller also has to tell the affected people directly, without undue delay.
This may be one of the most significant changes in practice for U.S. companies as they must comply with GDPR, since many U.S. state breach laws give companies weeks rather than hours.
According to the GDPR, companies that fail to comply can pay hefty fines for such behavior. The new requirements force companies to take data breaches more seriously and implement security measures to protect its data subjects.
9. Under GDPR, your organization is obligated to respond to a data subject’s request about their personal data.
GDPR gives consumers (i.e., data subjects) the right to ask companies for information held about them. Within a month’s time, companies must be able to fulfill the request, though that deadline can be extended by up to two more months for complex or numerous requests.
Data subject access requests force organizations to know where the data collected is at all times, what information is being collected, how it's being used by whom, and when it's being accessed.
If the consumer finds an error, the organization must correct it (called "rectification").
If the customer opts to invoke their "right to be forgotten," the company must erase their data (called "erasure"). If the consumer doesn't like how their personal data is collected and used, they can object.
As you can imagine, this is one of the most significant portions of the data protection law: It enforces transparency surrounding personal data and information that organizations store and process.
Bottom line? Organizations can no longer hide what they know.
Most U.S.-based organizations are behind when it comes to having this data at their fingertips. Big data is big, and it isn't always in the same place. Customer data can be in core operational systems, cloud applications, online file-sharing services, removable media, physical storage cabinets, temporary files, sandbox systems, backup systems, and employee devices (just to name a few).
Ultimately, gaining control over this data benefits both the organization and the consumer.
10. Consider appointing a data protection officer to stay GDPR compliant.
The General Data Protection Regulation requires some controllers and processors to appoint a data protection officer, or DPO.
This enterprise security leadership role is responsible for: overseeing a company's data protection strategy; monitoring data storage and data transfer operations; educating and training employees on regulatory compliance; implementing policies to support GDPR compliance; responding to data subject access requests; and serving as a point of contact between the organization and GDPR supervisory authorities.
You must appoint one if...
- Your organization is a public authority or body (courts acting in their judicial capacity are the exception)
- Your core activities involve regular and systematic monitoring of individuals on a large scale
- Your core activities involve large-scale processing of special categories of data (like health or biometric data) or data about criminal convictions
The size of your organization is irrelevant here. What matters is the size of your data processing operation and how effectively you implement data protection by design. But as you're probably thinking, "large-scale" is a nebulous term. The GDPR doesn't define it precisely, though EU regulators' guidance points to factors like the number of people affected, the volume and range of data, and the duration and geographic reach of the processing.
11. Cloud-based storage is not exempt from GDPR.
Like many organizations, you may use a cloud-based storage provider to house your data (like Microsoft Azure, Google Cloud, or Amazon Web Services). This practice does not off-load your data processing responsibilities to the cloud storage provider. Many organizations make the mistake of assuming their cloud storage providers are GDPR compliant, but that’s not always the case.
Under the GDPR, both controllers and processors carry obligations. You'll need a data processing agreement with your cloud provider (Article 28), and you're still responsible for how you configure and use the service — yet another reason it's helpful to have a data protection officer.
12. Under GDPR, human rights are prioritized over user experience.
Remember, the purpose behind GDPR is to protect consumers on data privacy issues. It's an ambitious, far-reaching piece of legislation designed to safeguard the public’s privacy and provide agency over their data.
There's no doubt that GDPR compliance creates challenges for all organizations, especially those that rely heavily on robust data processing. Compliance requires one-time and recurring costs, new policies and procedures, education and training, and even extra staffing.
Framers of the GDPR are aware of those challenges. Still, while they understand your frustration, they feel — and we agree — that the rights of the data subject are paramount, even at the expense of user experience. At a time when nearly every conceivable data point of our lives is stored online, we are remarkably vulnerable to theft and exploitation. Thus, we require concrete safeguards for better protection.
Read similarities and key differences between GDPR and CCPA.
GDPR Compliance FAQ
What does it mean to be GDPR compliant?
Being GDPR compliant means your organization meets the GDPR's requirements for every use of personal data about people in the EU: a lawful basis, transparency, respect for individuals' rights, appropriate security, timely breach reporting, and documentation that proves it.
Does the GDPR apply to U.S. companies?
Yes, if they offer goods or services to people in the EU or monitor their behavior, for example by tracking EU visitors on a website. A U.S. company with no EU customers and no monitoring of people in the EU generally falls outside its scope.
What are the 7 principles of GDPR?
Lawfulness, fairness, and transparency; purpose limitation; data minimization; accuracy; storage limitation; integrity and confidentiality; and accountability. They're set out in Article 5 and explained above.
How do I become GDPR compliant?
Start by mapping your personal data, choosing a lawful basis for each purpose, and updating your privacy notice. Then build processes for consent, data subject requests, vendor contracts, security, and breach response, and document everything. The 10 steps above walk through the order.
What are the fines for GDPR non-compliance?
Up to €20 million or 4% of worldwide annual turnover, whichever is higher, for the most serious violations, and up to €10 million or 2% for others. Regulators can also order you to stop processing data.
Is there an official GDPR certification?
The GDPR allows for approved certification schemes (Article 42), but there's no single, government-issued "GDPR certified" status. Holding a certification doesn't reduce your responsibility to comply.
You Don’t Have to Manage EU GDPR Requirements on Your Own
No matter the size of your organization, EU supervisory authorities can penalize your business for non-compliance with European data protection regulations. Yes, even small businesses fall across the GDPR radar.
Still, while it’s critical that you comply, the regulation is massive and complex. Osano helps you put the GDPR's requirements into practice without building everything from scratch.
We serve as your GDPR representative, monitor your vendors, help you respond to access requests, and alert you about new or changing privacy laws with advice on how to prepare. Let Osano make it simple. Are you a business in the US? Find out if the GDPR applies to the USA.
GDPR Compliance Checklist
GDPR compliance can seem pretty intimidating—especially if you’re trying to figure out where to start. Download this checklist to discover 8 steps to build your foundation.
Download Your Copy