The CCPA's right to delete has had a hole in it since the law took effect in 2020, and it was big enough to drive a data broker through.
Under the law as written, a business didn't have to delete personal information it got from a third party. You could file a deletion request, get the confirmation email, and the company could hang on to whatever it had bought about you from someone else. On Sunday, Governor Newsom signed SB 923, which closes that gap starting January 1, 2027. Deletion now reaches your data no matter how the business got it, and businesses can keep a suppression list so deleted people don't reappear with the next batch of third-party data.
For digital businesses, SB 923 had another significant change: online-only businesses are now required to feature a subject rights form on their website. CalPrivacy says that'll make requests simpler to submit, and I believe it: an email inbox is where a deletion request goes to be forgotten. A webform collects what you need up front and gets the request moving. It's also one more thing on your website a regulator can test, so it needs to work on day one. Don’t fall into the trap of wiring up a CMS form or support ticket form–you’ll just be asking for headaches down the road. Check out our writeup on SB 923 to learn why.
Not all things data privacy made it through–the same day, Newsom vetoed AB 1542, which would have banned the sale of sensitive personal information. He did sign AB 883, which gives data brokers 30 days instead of 45 to process deletion requests through DROP.
All together, this flurry of data privacy legislation is yet another example of how data privacy just doesn’t sit still.
Best,
Arlo
New From Osano
SB 923 and CCPA Webforms: How Subject Rights in California Just Changed
SB 923 updates how businesses subject to the CCPA must process deletion requests. Long story short? More data is in-scope, and businesses need to take extra steps to make it easy for consumers to submit deletion requests. Learn more and how to comply in our blog.
In Case You Missed It...
6 Product Updates to Make Your Privacy Program Easier
The Osano team’s been hard at work updating the platform–in fact, they’ve been working so much, we couldn’t pick just one update to update you on. Check out our post for the full summary.
Events
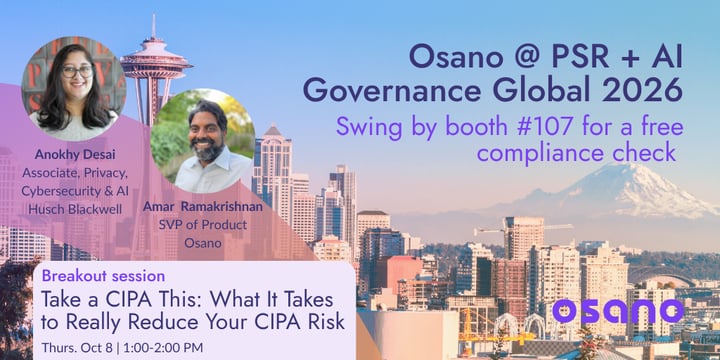
Speaking Session: Take a CIPA This: What It Takes to Really Reduce Your CIPA Risk
Attending IAPP’s Privacy. Security. Risk. + AI Governance Global 2026 conference this year? Don’t miss Osano’s Amar Ramakrishnan and Husch Blackwell’s Anokhy Desai as they break down how to *really* reduce CIPA risk. Come say hi to the Osano team at booth #107! Learn more and register below.
Top Privacy Stories of the Week
New Mexico Jury Finds Facebook Deceived Users About Privacy Protections
A Santa Fe jury found Facebook liable for deceiving users about how it protected their data in connection with Cambridge Analytica, which harvested data from roughly 87 million profiles through a third-party personality quiz. Jurors found more than 43 million violations of the state's consumer protection law, and New Mexico is asking for the maximum $5,000 per violation, which could top $200 billion.
44 Attorneys General Settle With Labcorp Over Its Debt Collector's Breach
A bipartisan coalition of 44 attorneys general reached a roughly $2.3 million settlement with Labcorp over the 2019 breach at American Medical Collection Agency (AMCA), the debt collector it used. That breach potentially exposed information on 27.5 million people, including 10.2 million Labcorp patients. The hack happened on AMCA's systems, but the states held Labcorp responsible for overseeing its vendor. The settlement requires Labcorp to share less data with debt collectors and to write cybersecurity requirements into their contracts.
Study: Your Car and Its App Are Sharing Data With Tech and Ad Companies
Researchers at Northeastern University and Consumer Reports tested 21 late-model vehicles from 17 automakers, plus 30 companion apps. Nineteen of the vehicles sent traffic to at least one third party. Seven apps passed sensitive data like VINs, emails, phone numbers, and precise location to companies tied to tracking and advertising. The data went to companies including Google, Meta, and Microsoft, and pairing the app with the car roughly doubled that exposure.
TikTok Drops Its Appeals, Making the UK's £12.7 Million Children's Privacy Fine Final
TikTok withdrew its appeal of the £12.7 million fine the ICO issued in 2023, after the UK Upper Tribunal rejected its argument that it processed children's data for "artistic purposes." The ICO estimated about 1.75 million UK children under 13 used TikTok in 2020, and found the company failed to get parental consent for them. TikTok also dropped a second appeal that had stalled the ICO's investigation into how its recommender systems use data from 13- to 17-year-olds, so that probe can now move forward.
Shoppers Complain to the ICO About Debenhams' 94-Box Unsubscribe Process
The ICO confirmed it has received complaints about the "complexity of Debenhams' unsubscribe process." One shopper said opting out meant unticking five boxes for each of the group's 15 brands, plus 19 more in the main Debenhams section. That's 94 boxes, and the shopper said the marketing emails kept coming anyway. The ICO hasn't confirmed a formal investigation, and Debenhams says the regulator hasn't contacted it.
Like What You See in the Privacy Insider newsletter?
There's more to explore:
🛠️ The Osano Engineering Blog
Learn what we're building, why, and how! New posts released monthly here.
📱 The Osano Subreddit
Join our official subreddit to stay up to date on the latest news, analysis, guidance, and content from Osano!
📖 The Privacy Insider: How to Embrace Data Privacy and Join the Next Wave of Trusted Brands
The book inspired by this newsletter: Osano CEO, Arlo Gilbert, covers the history of data privacy and how companies can start building a privacy program from the ground up. More details here.
If you’re interested in working at Osano, check out our Careers page!