Europe continues to contend with how it ought to modernize the GDPR, with opt-out signals serving as the most-recent lightning rod.
In November of last year, the European Commission’s proposed GDPR updates had two articles working together. Article 88a would have pulled the cookie consent rule out of the ePrivacy Directive and into the GDPR as one EU-wide standard, replacing the patchwork of national versions every member state has written since. Article 88b would have required sites to honor that browser-based tracking signals the moment a browser sent it. In effect, this would have required an EU Global Privacy Control (GPC), or universal opt-out preference signal.
But the Council dropped 88b back in June, and when noyb published the latest leaked draft this week, 88a was gone too.
Some commentators believed the original version would do away with cookie banners in the EU; it would not have. Article 88b’s signal was only ever going to help the people who went and turned it on, the same way the GPC works today. Everyone else was still going to see a banner, because GDPR's notice requirement doesn't go away just because a browser signal might exist.
What this new draft actually means–if it were to move forward–is that the patchwork of cookie banners across the EU stays in place. No convenient browser-based signal, no EU-wide consistency.
It’s important to recognize that none of this is final. It's a leaked negotiating draft. If you’ve been watching EU negotiations on GDPR modernization, you might be understandably frustrated with its glacial pace, the reversals, and leaks like this one. But I think this effort shouldn’t be easy or fast. Maybe it shouldn’t even be neat. The GDPR reshaped the internet, and that’s no understatement. GDPR 2.0 might be just as influential.
Best,
Arlo
New From Osano
6 Product Updates to Make Your Privacy Program Easier
The Osano team’s been hard at work updating the platform–in fact, they’ve been working so much, we couldn’t pick just one update to update you on. Check out our post for the full summary.
Events
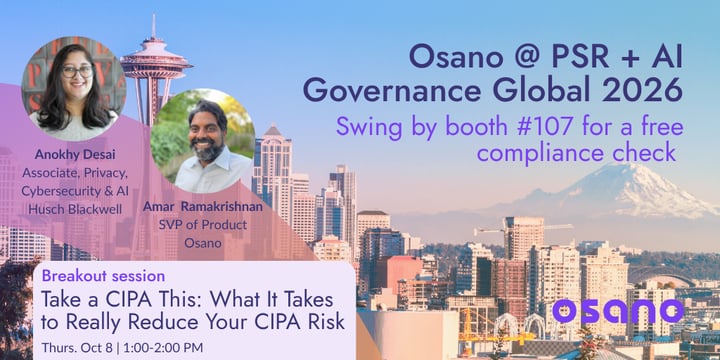
Speaking Session: Take a CIPA This: What It Takes to Really Reduce Your CIPA Risk
Attending IAPP’s Privacy. Security. Risk. + AI Governance Global 2026 conference this year? Don’t miss Osano’s Amar Ramakrishnan and Husch Blackwell’s Anokhy Desai as they break down how to *really* reduce CIPA risk. Come say hi to the Osano team at booth #107! Learn more and register below.
Top Privacy Stories of the Week
EU Council Drops Its Browser-Based Cookie Opt-Out Signal
A leaked Council of the EU compromise text shows both cookie provisions from the Commission's original proposal are gone. Article 88b, which would have required sites to honor a browser-based opt-out signal, was dropped in June. Article 88a, which would have moved cookie consent out of the ePrivacy Directive and into the GDPR as one unified standard, was cut from the latest text, dated September 3. Privacy group noyb published the leaked documents this week, and 19 organizations have written to EU institutions asking to restore the browser signal.
Texas AG Warns of Scam Demand Letters Over Website "Wiretapping"
Texas Attorney General Ken Paxton is warning businesses about a wave of demand letters accusing them of illegal "wiretapping" under California's Invasion of Privacy Act for using ordinary website tools like cookies, pixels, and search bars. Paxton's office singled out Vivek Shah, a self-described CIPA plaintiff since barred as a vexatious litigant in the Central District of California, as emblematic of who's behind the letters.
Google Fined €403 Million for Mishandling Location Data in the EU
Ireland's Data Protection Commission fined Google €403 million ($463 million) over how it handled location data in Web & App Activity, Location History, and Android's Location Accuracy feature between 2018 and early 2020. The regulator found Google lacked a lawful basis for the processing and wasn't transparent enough about it. The investigation took six years to close, and Ireland's DPC says three more privacy probes into Google remain open.
Sweden Fines HR Vendor Miljödata Over 2025 Ransomware Breach
Sweden's data protection authority fined HR software provider Miljödata about $183,000 after a 2025 ransomware attack exposed sick-leave records, rehabilitation details, and school incidents involving minors for 2.2 million people. Investigators found the company hadn't adequately tested new software before installing it and had no automated, real-time monitoring to catch intrusions. Miljödata's systems run HR operations for 80% of Sweden's municipalities, and regulators have separately opened investigations into two municipalities and a region over their own handling of the breach.
Philippines Orders Meta, Roblox, Reddit, and Discord to Explain Privacy Compliance
The Philippines' National Privacy Commission issued show-cause orders to Meta, Roblox, Reddit, and Discord, demanding they account for alleged non-compliance with the country's data-registration rules. The order lands alongside a separate 24-hour ultimatum from the national cybercrime agency telling Reddit and Discord to appoint local representatives or risk being blocked. Both actions follow a string of school shootings in the Philippines that investigators tied to radicalization and exploitation happening in unmonitored corners of these platforms.
Like What You See in the Privacy Insider newsletter?
There's more to explore:
🛠️ The Osano Engineering Blog
Learn what we're building, why, and how! New posts released monthly here.
📱 The Osano Subreddit
Join our official subreddit to stay up to date on the latest news, analysis, guidance, and content from Osano!
📖 The Privacy Insider: How to Embrace Data Privacy and Join the Next Wave of Trusted Brands
The book inspired by this newsletter: Osano CEO, Arlo Gilbert, covers the history of data privacy and how companies can start building a privacy program from the ground up. More details here.
If you’re interested in working at Osano, check out our Careers page!