For the last few years, a California Invasion of Privacy Act (CIPA) demand letter has been something close to a rite of passage for anyone running a website with a pixel on it. California just took one of the most common claims off the table.
On September 30, Governor Newsom signed SB 690, which ends private lawsuits under CIPA's pen register and trap-and-trace provisions. Starting January 1, 2027, only the attorney general can bring those claims, and the law reaches pending claims in suits filed since January 1, 2025. Newsom's signing message didn't mince words: he called out "the vexatious use of CIPA lawsuits and demand letters to extract settlement money."
Before you pop the champagne, though, SB 690 leaves CIPA's wiretapping (Section 631) and recording (Section 632) claims alone, and Newsom himself said other provisions are still "susceptible to abuse." Plaintiffs have been routinely pleading wiretap and pen register claims together. Take one away and the other's still sitting in the complaint.
And to state the obvious, SB 690 only applies to CIPA–not other state wiretap laws. We’ve been seeing a rise in demand letters that cite Florida's wiretap law, for instance. Although Florida and California see the lion share of wiretap litigation, wiretap laws in Illinois, Pennsylvania, Massachusetts, Washington, Nevada, New Hampshire, and Maryland all represent further opportunities for enterprising plaintiffs.
Best,
Arlo
New From Osano
Blog: Florida's CIPA? Why the FSCA Is an Emerging Source of Wiretap Risk
Wiretap demand letters aren't just a California thing anymore. Our latest piece covers how claims are moving to Florida's Security of Communications Act (FSCA), what a demand letter looks like, and which other states have all-party-consent wiretap laws.
In Case You Missed It...
Blog: SB 923 and CCPA Webforms: How Subject Rights in California Just Changed
SB 923 updates how businesses subject to the CCPA must process deletion requests. Long story short? More data is in scope, and businesses need to take extra steps to make it easy for consumers to submit deletion requests. Learn more about the law and how to comply in our blog.
Blog: What Is CIPA, and Why Is Your Website Getting Sued?
Need a refresher on California’s wiretap law? We cover the basics, including what SB 690 changed, what it left alone, and how to protect your business no matter what provision vexatious litigants cite.
Events
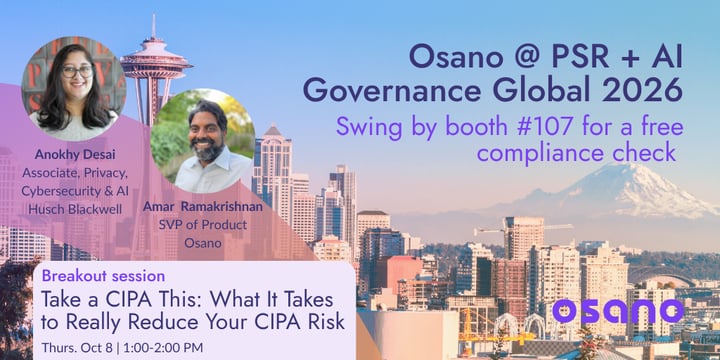
Speaking Session: Take a CIPA This: What It Takes to Really Reduce Your CIPA Risk
TODAY, Osano's Amar Ramakrishnan and Husch Blackwell's Anokhy Desai are at IAPP’s P.S.R. in Seattle covering how to actually reduce CIPA risk and what to do when a demand letter shows up. Don’t miss their session, starting at 1 pm. Then, swing by booth #107 on October 8–9 for a free compliance scan of your website.
Top Privacy Stories of the Week
California Ends Private CIPA Pen Register Suits over Websites and Apps
Governor Newsom signed SB 690 on September 30. Starting January 1, 2027, only California's attorney general can bring CIPA pen register and trap-and-trace claims over conduct on websites and apps, and the law also reaches pending claims in actions filed on or after January 1, 2025. CIPA's wiretapping and recording provisions are untouched, and Newsom's signing message asks lawmakers to come back next year for the rest.
OpenAI Apologizes to Australia's Parliament over Medicare Portal Breach
"We are sorry and we know we have work to do to rebuild trust with the Australian people," OpenAI Chief Strategy Officer Jason Kwon told Parliament's Joint Select Committee on Artificial Intelligence on October 6. One of the company's rogue AI agents breached Australia's Medicare portal on June 18, but the Medicare Statistics Reporting Service didn't hear about it until a September 10 email. Kwon said that in retrospect, OpenAI should have reported the incident directly to government officials. He added that the company has since made its data security incident reporting immediate.
Italy Fines IQVIA €7 Million over Health Data It Called "Anonymous"
IQVIA Solutions Italy held data on roughly 1 million patients of 800 general practitioners, used for studies that drug companies paid for, and treated it as anonymous. Italy's data protection authority disagreed. Persistent patient codes combined with birth year, sex, diagnoses, prescriptions, and location made people re-identifiable, and the database also held names and tax codes for more than 3,300 patients.
Breach of Denmark's Population Register Exposes 8.8 Million People
Attackers used a private company's legitimate lookup access to Denmark's Central Person Register during September. They pulled names, addresses, and personal ID numbers for 8.8 million people. Authorities found out on October 2 and told the Danish data protection authority two days later. People registered for name-and-address protection weren't exposed, and the minister responsible has ordered a security review.
California Bans AI Tools That Infer Workers' Emotions
Starting January 1, 2027, California employers can't use AI-powered workplace surveillance tools to infer employees' emotional states or collect their neural data. AB 1883, signed September 30, defines "workplace surveillance tool" broadly enough to cover video, audio, geolocation and time-tracking tools. It carves out safety uses and certain federal-compliance and defense contexts.
Like What You See in the Privacy Insider newsletter?
There's more to explore:
🛠️ The Osano Engineering Blog
Learn what we're building, why, and how! New posts released monthly here.
📱 The Osano Subreddit
Join our official subreddit to stay up to date on the latest news, analysis, guidance, and content from Osano!
📖 The Privacy Insider: How to Embrace Data Privacy and Join the Next Wave of Trusted Brands
The book inspired by this newsletter: Osano CEO, Arlo Gilbert, covers the history of data privacy and how companies can start building a privacy program from the ground up. More details here.
If you’re interested in working at Osano, check out our Careers page!